| Title: Persistent XSS in wordpress plugin rockhoist-badges v1.2.2 |
| Author: Larry W. Cashdollar, @_larry0 |
| Date: 2017-02-20 |
| CVE IDs:[CVE-2017-6102] |
| Download Site: https://wordpress.org/plugins/rockhoist-badges/ |
| Vendor: |
| Vendor Notified: 2017-02-20 |
| Vendor Contact: |
| Advisory: http://www.vapidlabs.com/advisory.php?v=176 |
| Description: A Stack Overflow inspired plugin for WordPress which allows users to acquire badges for contributing website content. Badges are created and managed through the WordPress Dashboard. |
| Vulnerability: There is a persistent cross site scripting vulnerability in the plugin Rockhoist Badges. A user with the
ability to edit_posts can inject malicious javascript. Into the badge description or title field.
Line 603 doesn't sanitize user input before sending it to the browser in file ./rockhoist-badges/rh-badges.php:
-> 603: <span class="delete"><a href="?page=badges&action=deletecondition&badge_ID=<?php echo $_GET['badge_ID']; ?>&badge_condition_ID=<?php echo $badge_condition->badge_condition_id; ?>" class="delete-tag">Delete</a></span>
|
| Export: JSON TEXT XML |
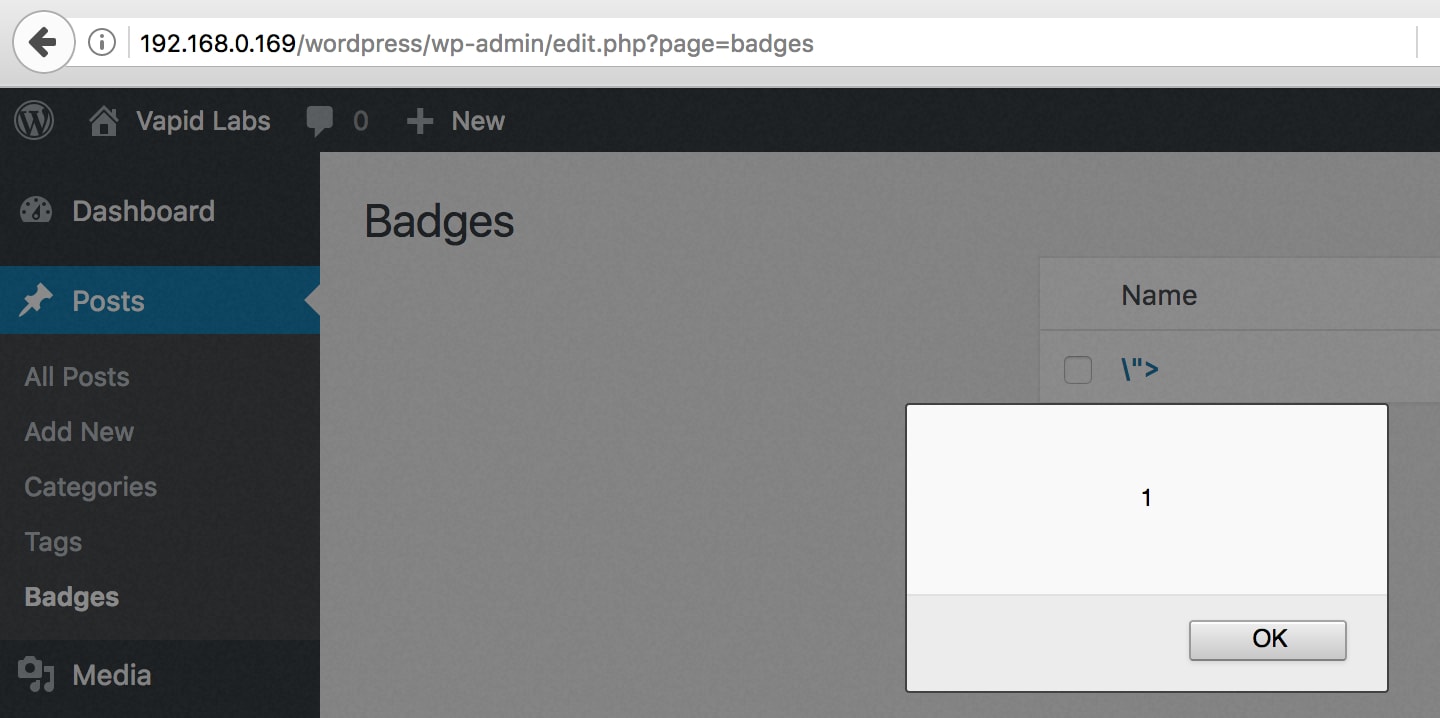
| Exploit Code: "> in the title or description field will inject js. |
| Screen Shots: [badges.jpg] |
| Notes: |